
Web Application Firewall (WAF) Integration
-
0 sales
- 284 views
- Save
0 /5.0
User review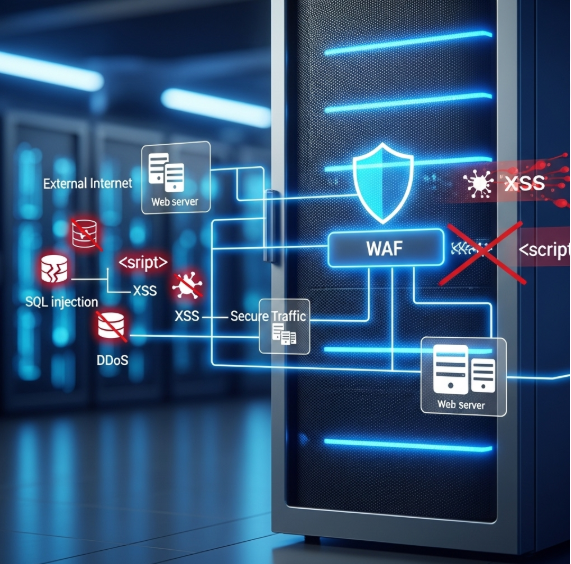
Web Application Firewall (WAF) Integration – Full Scope
1. Discovery & Assessment
- Audit existing web applications, servers, and network architecture
- Identify security requirements and regulatory compliance needs (PCI DSS, GDPR, HIPAA)
- Map application traffic patterns, APIs, and potential threat vectors
- Assess current security controls and gaps
2. WAF Strategy & Planning
- Define protection goals: block SQL injection, XSS, DDoS, bot attacks, and other OWASP Top 10 threats
- Select appropriate WAF deployment model: cloud-based, on-premise, or hybrid
- Establish policies for traffic inspection, rule sets, and threat mitigation
- Determine integration with SIEM, monitoring, and alerting systems
3. Implementation & Configuration
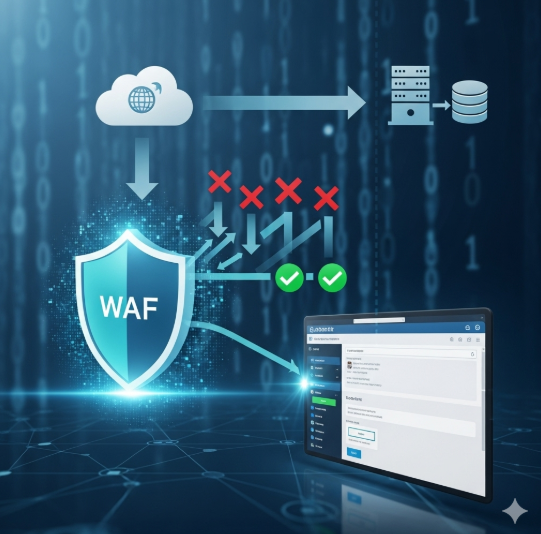
- Deploy WAF at the network edge, load balancer, or application level
- Configure custom rules, signatures, and rate limiting based on application behavior
- Enable SSL/TLS termination and secure traffic inspection
- Integrate with authentication, API gateways, and backend systems
4. Monitoring & Logging
- Capture real-time traffic logs and security events
- Configure alerts for suspicious activity, rule violations, or potential breaches
- Integrate with centralized logging and analytics platforms for visibility
5. Testing & Tuning
- Conduct security testing, penetration tests, and vulnerability scans
- Fine-tune rules to minimize false positives and ensure legitimate traffic flow
- Continuously monitor attack patterns and adjust rules accordingly
6. Compliance & Reporting
- Maintain audit logs and reporting for regulatory compliance
- Generate detailed reports on blocked threats, incidents, and mitigation actions
- Ensure alignment with security policies and industry standards
7. Maintenance & Optimization
- Regularly update WAF signatures, rules, and threat intelligence feeds
- Monitor application changes and adapt WAF policies accordingly
- Provide training and documentation for security and IT teams
- Continuously optimize for performance, availability, and threat coverage
8. Value Delivered
- Real-time protection against web application attacks and vulnerabilities
- Enhanced visibility into traffic and security events
- Compliance with industry standards and regulatory requirements
- Reduced risk of data breaches, downtime, and reputational damage
- Scalable and adaptable security framework for evolving web applications
Additional services
-
0 $
-
0 $
-
0 $
-
0 $
-
0 $